


















Data Discipline Demanded: EC Warns Against Unauthorized NID Access
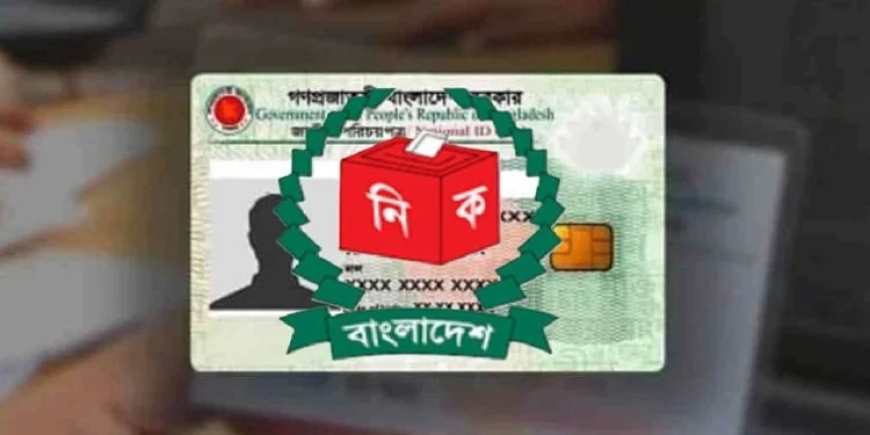
The Election Commission (EC) has issued a stern warning against unauthorized access to the National Identity (NID) server, which holds the personal information of approximately 123.7 million registered voters across Bangladesh. Any individual or organization accessing this data without permission will face strict administrative and legal action, the Commission has announced.
Engineer Mohammad Ariful Islam, Systems Analyst at the EC, issued an official notice to all secretariat and field-level staff, alerting them about unauthorized use of the Card Management System (CMS). The directive states that some CMS users have been accessing citizens’ information through their designated accounts and supplying it to unauthorized individuals or organizations for personal gain — a practice the EC deems illegal.
“Each search made within the CMS — including who made the search, when, and from which account — is automatically logged on the server,” the directive explains. “Therefore, identifying unauthorized or malicious inquiries is possible. If such actions are proven, the Commission will not hesitate to take action against those involved.”
As such, all CMS account holders have been urged to strictly adhere to the EC’s data access protocols. The EC emphasized that any data used during application processing must only be accessed by designated and authorized personnel.
Earlier in February, EC Secretary Akhtar Ahmed revealed that five institutions had leaked NID information to third parties. A preliminary investigation found evidence of data breaches involving the Directorate General of Health Services, Upay (a concern of UCB Bank), the Chattogram Port Authority, the Department of Women Affairs, and the iBAS system of the Ministry of Finance.
In response, Director General of the National Identity Registration Division, A.S.M. Humayun Kabir, announced plans for surprise inspections of organizations using NID verification services to curb further leaks.
Currently, 182 institutions are authorized to verify NID data with the EC. However, there have been allegations that some institutions have been violating contract terms by sharing access with other entities. The EC has since reviewed the data access requirements of these institutions and held a series of meetings to enforce stricter compliance.